AI agents are forcing enterprises to rethink authorization and access control from first principles.
Traditional access control systems were designed for humans operating relatively predictable software, where workflows, permissions, and responsibilities could largely be defined in advance.
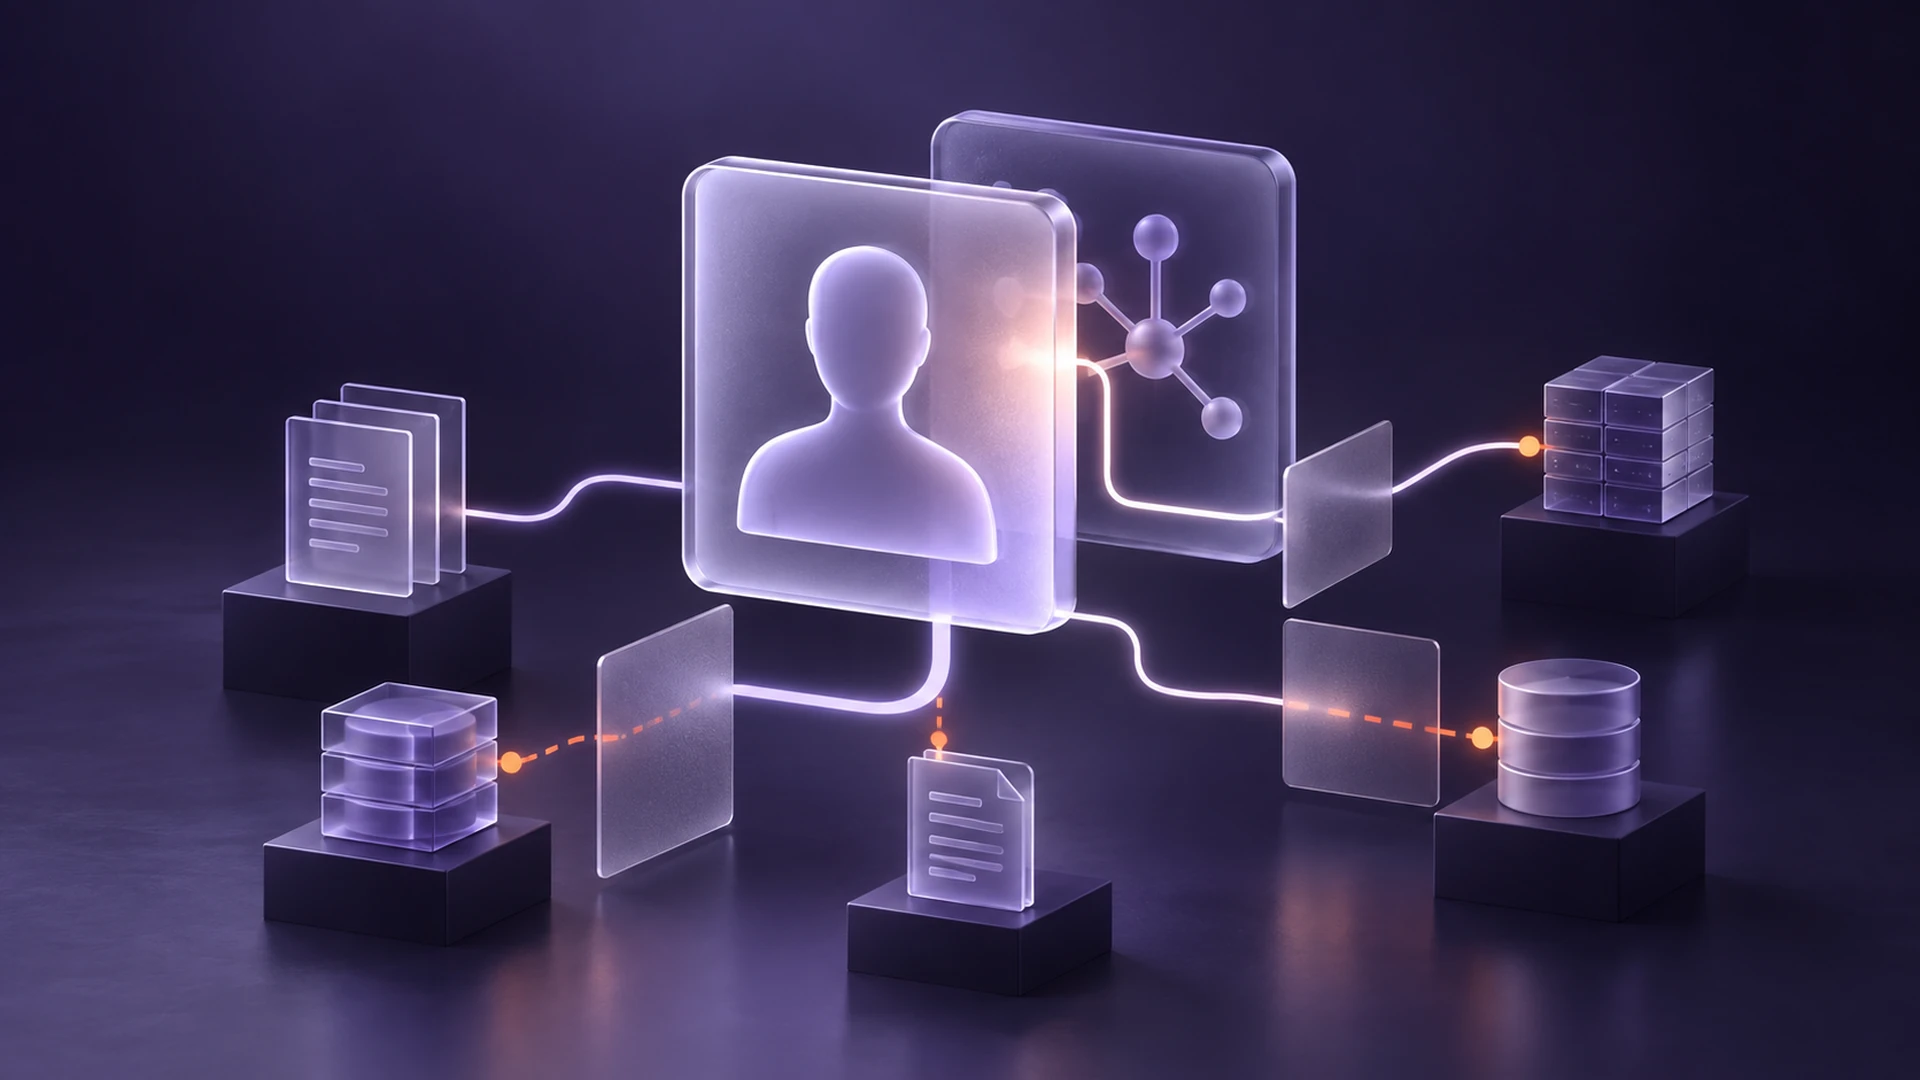
Autonomous AI agents behave very differently. They dynamically compose workflows, invoke APIs, retrieve information across systems, interact with MCP servers, and adapt their execution paths in pursuit of an objective. In these environments, authorization decisions need to account for why an action is being taken and whether it remains consistent with the agent’s intended task.
Intent-based access control (IBAC) makes that purpose part of the authorization decision. It evaluates whether a requested action fits the approved task, alongside identity, existing permissions, and enterprise policy.
As enterprises move from simple AI assistants toward fully agentic systems, one architectural question is becoming central: How do we control what AI agents are allowed to do?
Why standing role permissions alone are insufficient for AI agents
Many enterprise security architectures rely heavily on role-based access control (RBAC). Users are assigned roles, roles are mapped to permissions, and systems enforce access accordingly.
That model works well where responsibilities and access patterns are stable. With AI agents, however, a single workflow may span tools, APIs, MCP servers, and internal systems, with access needs that change as the work unfolds.
This creates several challenges for authorization based on standing role permissions alone.
Access decisions increasingly depend on the specific objective of the current workflow. The same agent may legitimately require broad access for one task and highly restricted access for another.
To avoid workflow failures, agents may be granted broad standing access across multiple systems and tools. Those permissions can exceed what any individual task requires, increasing the risk of inappropriate access and use.
Attempting to express every task-specific variation through increasingly granular roles can also become difficult to manage. As organizations scale the number of agents, MCP integrations, tools, and autonomous workflows, the number of role combinations grows.
Roles remain useful for defining authority. Agents also need controls that evaluate how that authority is used at each step of a workflow. Intent-based access control adds that task-specific constraint.
What is intent-based access control?
Intent-based access control is an authorization approach that evaluates whether an action is justified within the context of an agent’s current objective, execution state, and intended use of data or capabilities.
Alongside identity and permissions, IBAC evaluates whether a requested action is consistent with the approved purpose of the workflow. Intent becomes a constraint on authorization, supported by existing policy and identity signals.
In practice, decisions can draw on workflow state, delegation chains, data sensitivity, operational context, and prior actions within the same execution.
For example, permission to read customer records does not mean every customer record is relevant to a request to summarize one account. Intent helps define which access belongs within that task.
Why AI agents need intent-based access control
In agentic systems, execution is a sequence of decisions across tools, APIs, and sometimes multiple agents. Each step depends on the evolving state of the workflow.
An operation may be permitted by an agent’s standing credentials yet fall outside the task it was asked to complete. Evaluating intent helps distinguish between the two.
Authorization therefore needs to preserve the connection between each action and the approved objective. Relevant context includes:
- Who initiated the task.
- The active delegation chain across agents.
- Current workflow state.
- The specific resources being accessed.
- Previous agent actions.
- The intended use of each tool or capability.
With these inputs, the system can evaluate whether each action still belongs within the approved task. If work passes to another agent, that delegation should preserve the original constraints rather than expand access.
Intent-based access control brings task purpose into fine-grained authorization and runtime enforcement. Its value depends on carrying that purpose through execution, where individual access decisions are made.
MCP and autonomous AI workflows make intent even more important
The Model Context Protocol (MCP) allows agents to discover and interact with tools and resources exposed by connected servers. This flexibility helps agents work across systems, but it also creates more decisions about which capabilities they should use.
During execution, an agent may encounter a tool that appears useful but was not anticipated in the original workflow. Its availability does not establish permission to use it.
Intent-based controls provide a way to evaluate the proposed action against the approved task and enterprise policy. The decision needs to account for the resource and operation involved, as well as the identity of the agent making the request.
As workflows become more dynamic, maintaining that connection between purpose and action becomes increasingly important.
Intent-based access control with IndyKite
IndyKite brings intent-based access control into the execution of agent workflows, connecting the purpose of a request to decisions about data access, tool use, and delegation. Its Intent Agent translates natural-language requests into structured authorization statements, while AgentControl provides the policy enforcement points where those requests can be evaluated. Together, they help enterprises give agents the access needed to complete a task while keeping their actions within the authority of the user and the boundaries of enterprise policy.
The future of AI access control is intent-aware
AI agents are not traditional software components. They are autonomous execution systems operating toward objectives. As enterprises move deeper into agentic architectures, authorization models must evolve accordingly to facilitate appropriate access while protecting data and systems.
Identity still matters. Policies still matter. Least privilege still matters. But in AI systems, understanding the intent and execution context behind an action is becoming as important as identifying who initiated it.
Intent-based access control enables AI agents to scale while ensuring appropriate governance, and security. As AI agents become increasingly capable, intent-aware authorization is emerging as a foundational building block of enterprise AI security.
To learn more about how these ideas can be implemented in real agentic systems, including policy enforcement points, delegation chains, and MCP-aware controls, check out the AgentControl architecture guide.