AI is changing everything, but the way we secure, trust, and control data hasn’t kept up.
We’ve seen this pattern before. DevOps changed how we deploy. DevSecOps changed how we protect.
Now we’re entering the next shift. One where developers take control of how data is trusted and governed, not just how it’s stored or moved.
DataTrustOps? Call it what you want, it’s happening.
Control freaks welcome.
The next movement for builders
Movements start when builders get frustrated enough to fix what’s broken.
Right now, that frustration is bubbling up around AI.
Developers are asking:
- Why is every model connected to an untrusted data lake?
- Why can’t I tell what my AI really has access to?
- Why do we still treat authorization as an afterthought?
The answers all point in one direction: context. We can’t trust what we can’t understand and we can’t secure what we can’t contextualize.
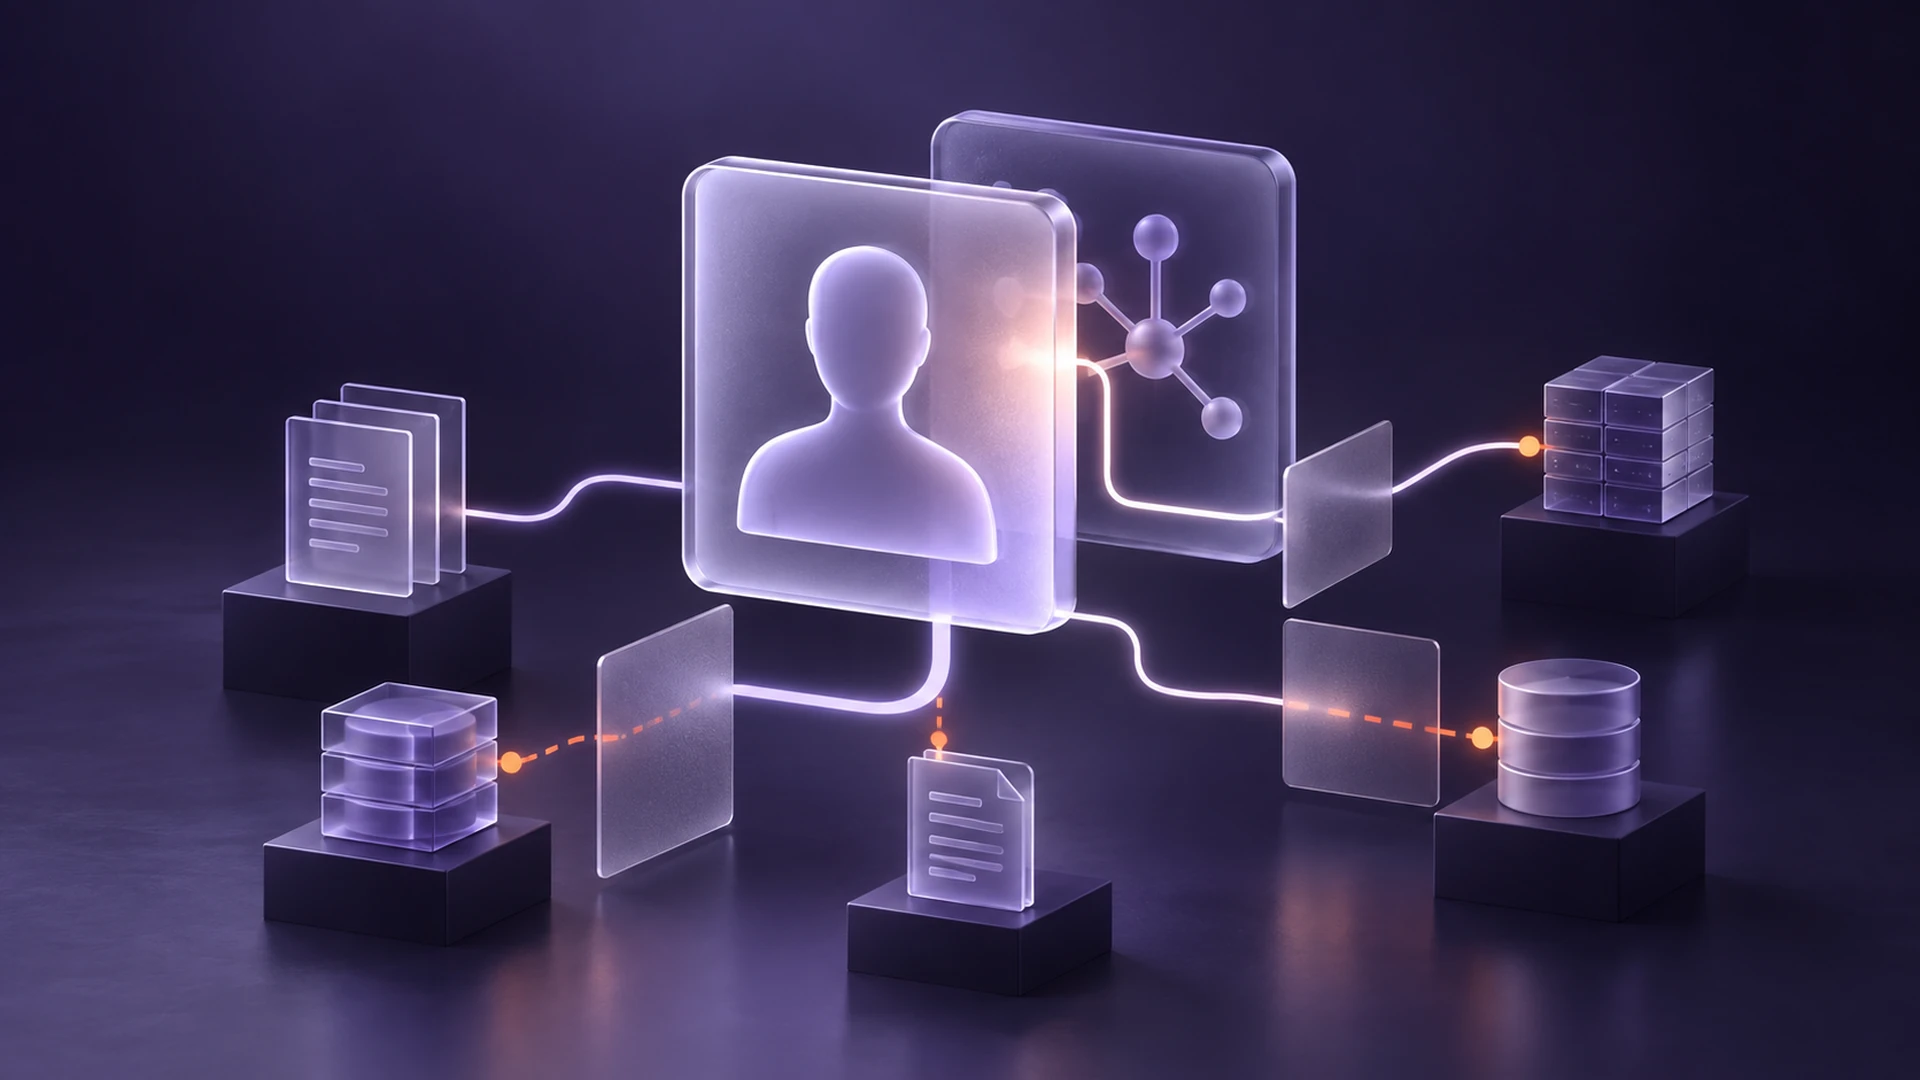
That’s the core of what IndyKite is building - a trust and control layer that combines context, identity and access.
It gives your applications and AI systems the same reasoning power about who, what, and why that humans use intuitively.
Trust in action
Here’s what that looks like in code:
That trustScore isn’t just metadata — it’s the difference between safe and catastrophic.
It’s computed from identity, lineage, and context — in real time.
When trust becomes a query parameter, you stop hoping your data is safe and start knowing it is.
That’s control.
From tooling to movement
This isn’t about one SDK, API, or policy engine.
It’s a cultural reset, giving developers the power and mental models to think trust-first and control-native.
That’s how you future-proof everything you build, whether it’s a RAG pipeline, an agent, or a customer-facing app.
When trust and control are baked into how data moves, every system becomes more explainable, auditable, and intelligent.
That’s what we’re building at IndyKite: a platform where trust, identity, and access are native building blocks not bolted on.
Join the builders of the trust layer
The people who built DevOps changed how software ships.
The people who build with IndyKite will change how AI and data decide.
We’re inviting you to be part of that movement.
👉 Explore our sandbox
👉 Share your experiments
Let’s make the future ready for what’s coming next.
Because when the world runs on AI — trust is the new runtime.
Control freaks welcome.