Everyone’s securing the model. No one’s securing the data behind it.
That’s the blind spot we see in today’s AI race and the reason IndyKite exists.
We’re seeing incredible progress in AI, from Retrieval-Augmented Generation (RAG) to autonomous agents that reason, recall, and respond. But underneath all of that brilliance is a fragile foundation: untrusted data. AI systems can only be as safe, compliant, and intelligent as the data they’re allowed to touch. Right now, most can’t tell the difference between “authorized” and “accidentally exposed.”
It’s time to fix that from the bottom up!
Everyone’s securing the model
AI security today is obsessed with the surface layer - from scanning for prompt injections to checking LLM weights. But the real risk starts much earlier.
If an AI pulls data it shouldn’t have access to, the model isn’t the problem. The missing trust layer is.
When your data layer doesn’t know context — who’s asking, what they’re allowed to see, why the request is happening — everything becomes guesswork. And that’s how sensitive information leaks into responses, embeddings, and memory stores.
The shift: Security starts at the data layer
We built IndyKite because we believe trust has to be computed, not assumed.
The future of security isn’t another firewall or AI scanner. It’s data trust and the ability to know in real time whether a request is authorized, contextual, and safe.
This is where the next generation of developers come in!
If you’re building AI pipelines, microservices, or RAG backends, you hold the keys to how trust is enforced. Every query, API call, and data retrieval can be instrumented with context-aware authorization.
Here’s a simple illustration:
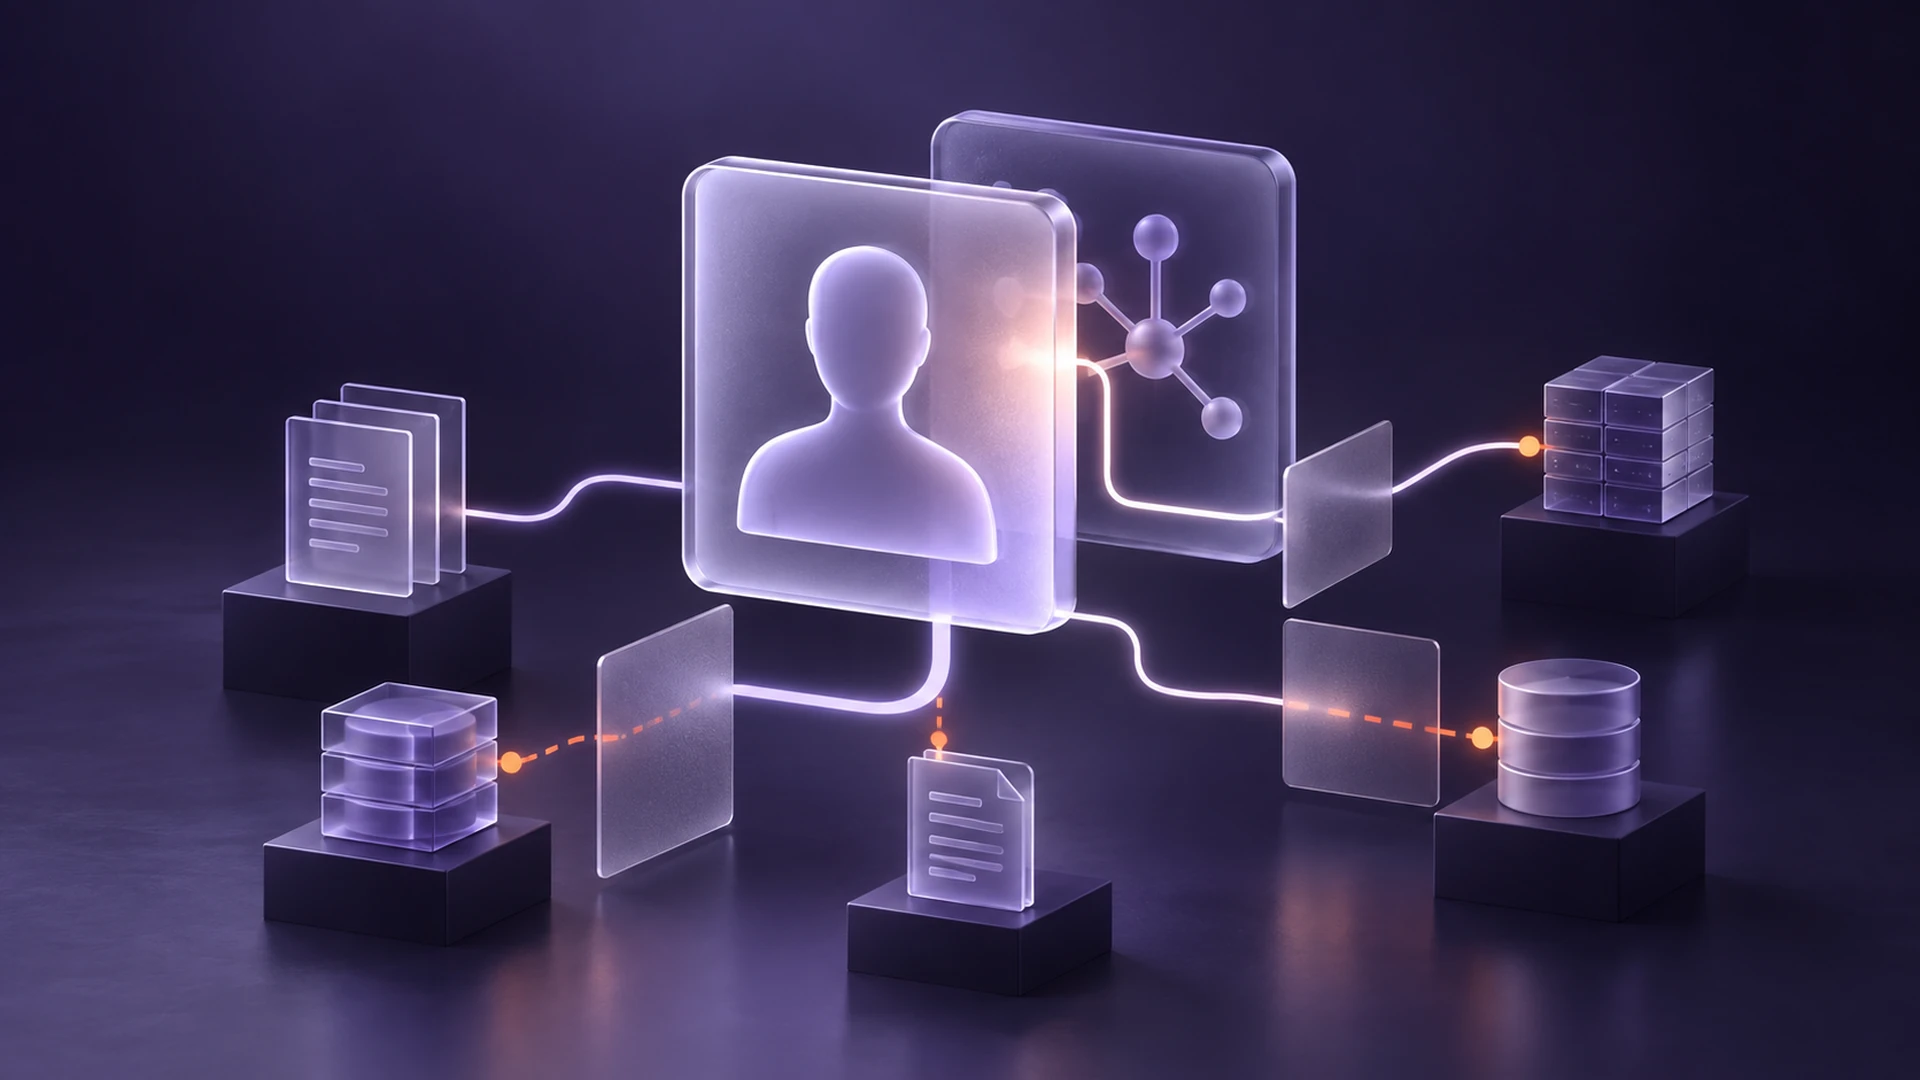
This isn’t “just another access control check.” Think of it as a trust computation, an evaluation of who the actor is, what they’re asking for, and why it should be permitted. Context isn’t limited to static attributes; it’s also defined by what the Subject and Resource are connected to in the graph. Policies can traverse those relationships to fetch the right context. For example, confirming that the Subject is part of Department X before granting access. That connected context makes all the difference.
The movement: Data trust by design
We’re not launching another developer tool. We’re starting a movement for AI and apps that can actually be trusted, systems that reason about access and data with the same intelligence as their outputs.
If DevOps made shipping faster and DevSecOps made it safer, DataTrustOps (not a thing yet…should we make it one?!) will make it responsible. It’s where developers take ownership of how trust is designed, built, and enforced - not just patched later.
At IndyKite, we’re giving developers the framework, SDKs, and examples to make that shift real. From specialized metadata to dynamic authorization, we’re equipping you to build AI systems that don’t just generate, they govern in real-time.
The ask: Join the builders of the trust layer
We’re calling on every developer building with AI, data, or identity to help shape this next paradigm. Share your stories. Break things. Test ideas. Build demos that prove AI doesn’t have to be a black box.
Trust isn’t a feature. It’s a foundation.
Let’s build it right this time.