Your AI agent isn’t the problem. Your AI model is generally not the problem…but the data?
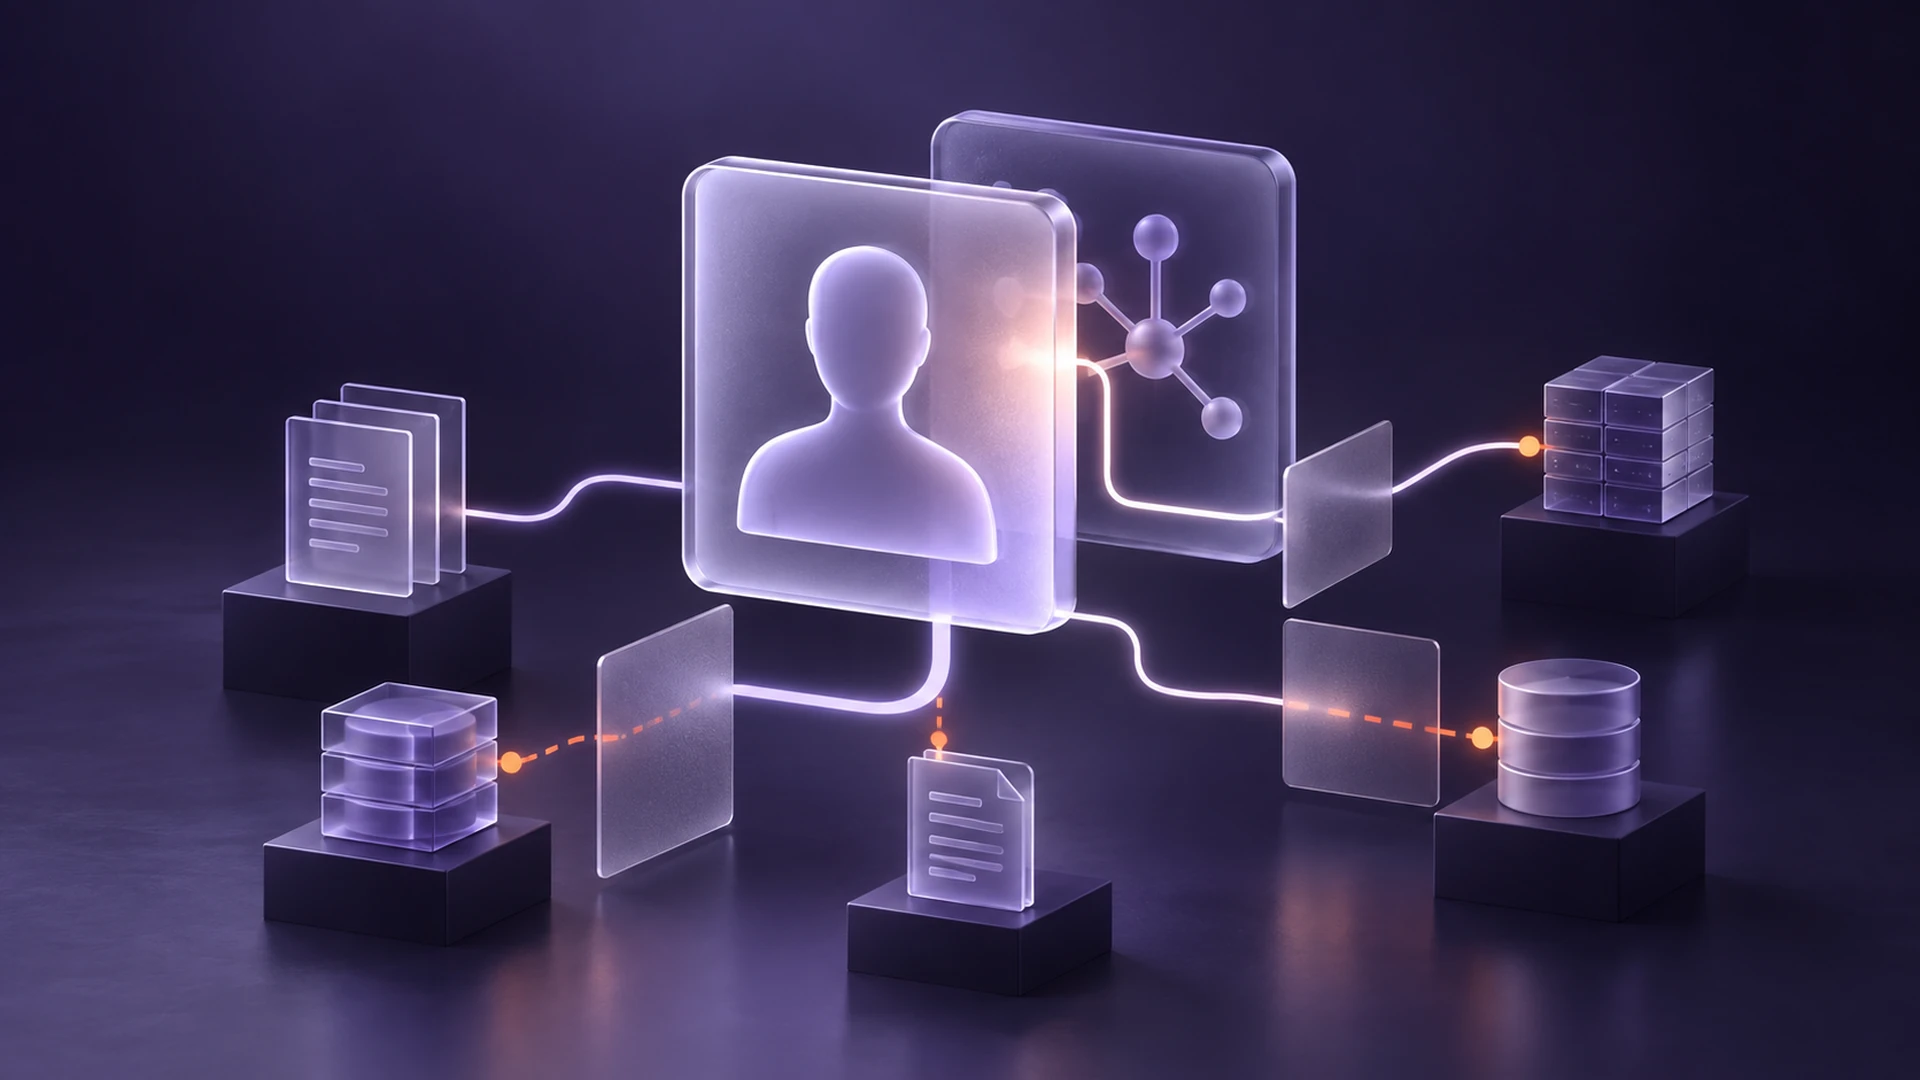
We’ve said it before: everyone’s securing the model. Few are securing the data layer — the hidden infrastructure that feeds RAGs, embeddings, and autonomous agents.
In our experience at IndyKite, AI agents often have access to more than they should. They can query knowledge graphs, vector stores, or APIs and pull in sensitive information simply because there’s no trust enforcement at the source.
The solution? Data trust through a foundational layer where access, context, and identity converge to give AI agents and apps the reasoning they need to operate safely.
The blind spot in AI security
Developers often focus on:
- Fine-tuning prompts
- Monitoring outputs
- Detecting injection attacks
All necessary, but incomplete. Without trust at the data layer, even well-designed agents can access data they shouldn’t, leading to leaks or compliance violations.
Implementing trust for AI agents
Trust is computable. It’s actionable. And it should be enforced at query time, not bolted on later.
Example: filtering sensitive data dynamically before it reaches an AI agent:
This prevents AI agents from accidentally seeing or exposing data they shouldn’t.
Why developers matter
Every AI agent is autonomous. Treating them like “just another user” is risky. By enforcing data trust, you:
- Protect sensitive information automatically
- Maintain regulatory compliance
- Make AI systems auditable and explainable
Trust becomes a runtime property, not an afterthought.
The movement continues
Data trust isn’t a feature. It’s a mindset shift.
At IndyKite, we’re giving developers the frameworks and tools to build trust-first AI so autonomous agents behave responsibly.