Product
Intent-Based Access Control
Fine-grained access control to filter target MCP tools or A2A Agent skills based on user intention.
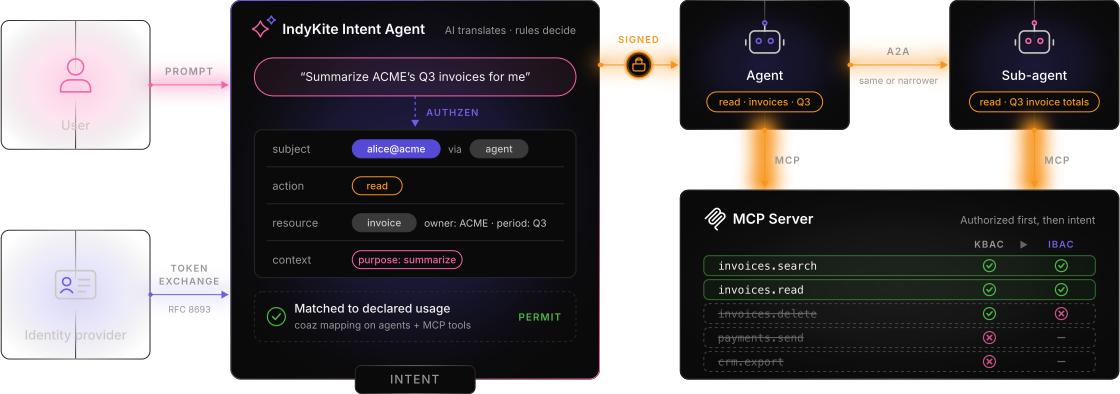
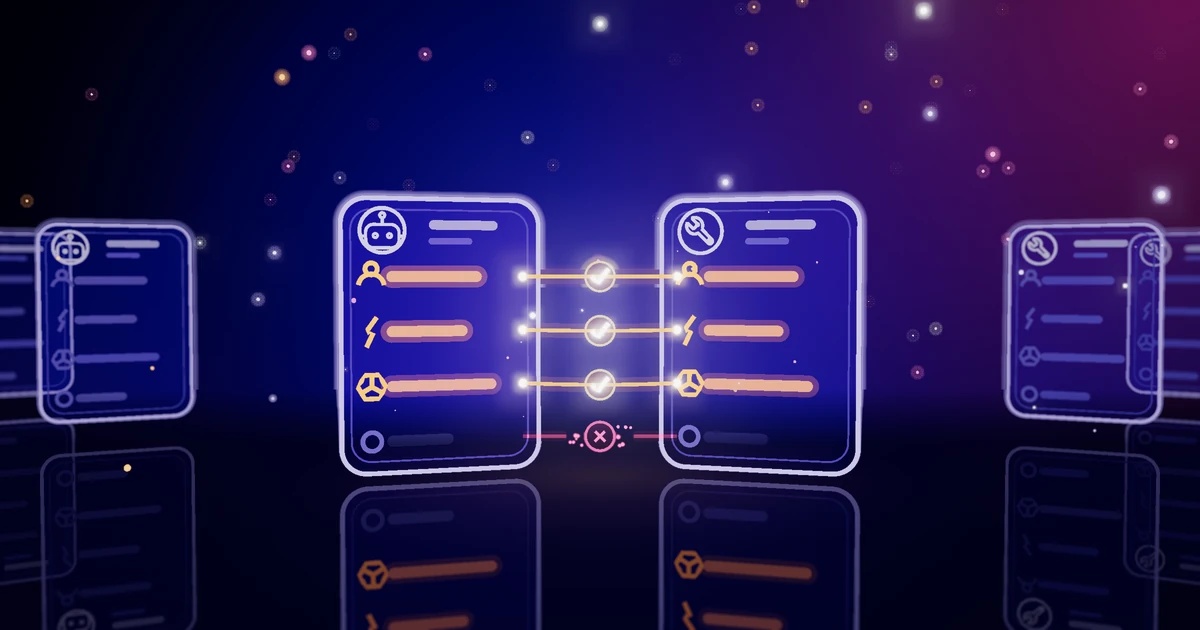
Intent-Based Access Control uses structured intent, carries it across every agent and tool, and enforces it at every step. Agents get exactly the access their task needs, and nothing more.
Delegation tells you who the agent acts for. Intent limits it to what they asked for.
On-behalf-of delegation gives an agent its own identity and lets it act for a person. On its own, it also hands that agent the full breadth of the person’s permissions and passes them down every hop of a multi-agent workflow. IBAC builds on the on-behalf-of model and identity providers you already run, and scopes the agent’s authority to the single task the person asked for.
IndyKite Intent Agent
AI translates and rules decide
Turn plain-language prompts into strict, enforceable authorization. A structured intent can be evaluated, repeated and audited. The same request gets the same answer every time, and every decision can be proven after the fact
Plain language to AuthZEN
Matched to declared usage
Enforceable by design
Open source so any team can adopt a standard way to express intent.
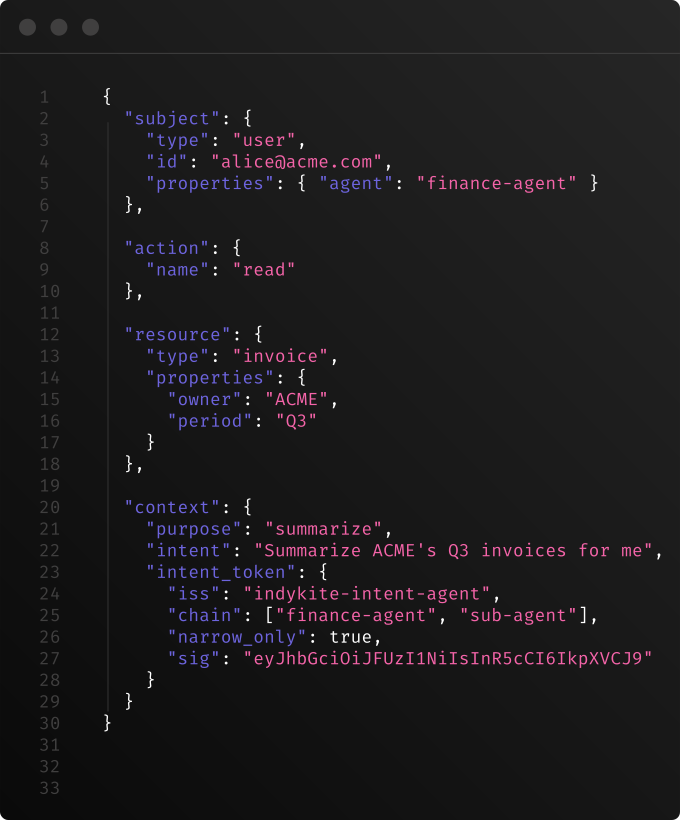
AI gets the access its task needs, at every step of the workflow.
Prevention, not detection
Provable decisions
Full traceability
Contained blast radius
No rebuilds
Open standards
Give your agents the autonomy to perform
Apply live context and control to every AI agent.